Audit Result
UUID: 01a096c8-aa9a-7364-843e-151622daed59
https://mamsm-dev.github.io/mam-tools/
Scanned 1 month ago
Meta Information
-
Title Tag Warning
Found 9 characters. Keep title between 30 and 60 characters.
Fix: Add a unique <title> tag describing the main page intent in 30-60 characters.
-
Meta Description Pass
Found 117 characters. Good snippet length.
-
Canonical URL Pass
Canonical found: https://mamsm-dev.github.io/mam-tools/
-
-
Viewport Meta Pass
Viewport configured: width=device-width, initial-scale=1.0
-
HTML Lang Pass
Language declared as "en".
Content Structure
-
H1 Tag Pass
Exactly one H1 found: "MAM Tools".
-
Heading Hierarchy Pass
Valid heading flow across 1 headings.
-
Image Alt Text Pass
All 0 images include alt text.
Technical Optimization
-
HTTPS Pass
Page is served over HTTPS.
-
HSTS & HTTPS Redirect Warning
2 HTTPS hardening issues detected.
- • HSTS is missing includeSubDomains.
- • Could not probe the HTTP version of this page.
- • Strict-Transport-Security: max-age=31556952
Fix: Set Strict-Transport-Security with a long max-age, add includeSubDomains, and redirect all HTTP requests to HTTPS.
-
Security Headers Warning
Missing: content-security-policy, x-frame-options, x-content-type-options, referrer-policy.
Full HTTP headers (23)
- • accept-ranges: bytes
- • access-control-allow-origin: *
- • age: 0
- • cache-control: max-age=600
- • content-encoding: gzip
- • content-length: 928
- • content-type: text/html; charset=utf-8
- • date: Sat, 12 Sep 2026 18:02:07 GMT
- • etag: W/"6aa155ae-a8e"
- • expires: Sat, 12 Sep 2026 18:12:07 GMT
- • last-modified: Wed, 09 Sep 2026 12:48:46 GMT
- • server: GitHub.com
- • strict-transport-security: max-age=31556952
- • vary: Accept-Encoding
- • via: 1.1 varnish
- • x-cache: MISS
- • x-cache-hits: 0
- • x-fastly-request-id: f5580deb946d6c48a4eef47f61f77311f708f380
- • x-github-edge-region: iad
- • x-github-request-id: 5636:3C17D9:7132DA:8E19C3:6AA5939F
- • x-proxy-cache: MISS
- • x-served-by: cache-iad-khef600094-IAD
- • x-timer: S1789236127.146094,VS0,VE50
Fix: Add the missing security headers at your reverse proxy or application layer.
-
CSP Quality Warning
Content-Security-Policy header is missing.
- • Missing Content-Security-Policy header.
Fix: Define a restrictive Content-Security-Policy and avoid unsafe directives such as unsafe-inline and unsafe-eval.
-
Cookie Security Pass
No first-party cookies were set during the initial page load.
-
Server response headers do not expose version tokens.
-
Cloudflare Proxy Warning
Domain does not appear to be behind Cloudflare.
-
Perceived Load Time Pass
Loaded in 0.24s (perceived).
-
Render Blocking Resources Warning
0 scripts and 1 styles may block rendering.
- • style: https://mamsm-dev.github.io/mam-tools/assets/index-CeJDrK3R.css
Fix: Defer non-critical scripts and inline critical CSS to improve first paint speed.
-
Compression Pass
Text-like assets appear compressed.
-
Robots.txt Error
robots.txt missing or inaccessible (404).
Fix: Create a robots.txt file at https://mamsm-dev.github.io/robots.txt and allow intended crawlers.
-
Sitemap File Warning
Sitemap missing or inaccessible at https://mamsm-dev.github.io/sitemap.xml (404).
Fix: Publish a sitemap.xml and reference it in robots.txt with: Sitemap: https://mamsm-dev.github.io/sitemap.xml
-
Crawl Directives Pass
Robots meta found: index, follow
Accessibility Basics
-
Form Labels Pass
All 2 controls are labeled.
-
Landmarks Warning
Missing landmarks: nav, footer.
Fix: Use semantic regions (<header>, <nav>, <main>, <footer>) for navigation and assistive tech.
-
Tap Target Size Warning
15 interactive elements appear smaller than 48px.
- • button.p-2.rounded-lg (Switch to dark mode) - 36x36px
- • button.px-4.py-2 (Text) - 58x36px
- • button.px-4.py-2 (File → Base64) - 124x36px
- • button.px-4.py-2 (Base64 → File) - 124x36px
- • button.px-4.py-2 (Hash) - 65x36px
- • button.px-4.py-2 (QR Code) - 90x36px
- • button.px-4.py-2 (base64) - 79x36px
- • button.px-4.py-2 (hex) - 57x36px
- • button.px-4.py-2 (binary) - 72x36px
- • button.px-4.py-2 (Encode) - 79x36px
- • button.px-4.py-2 (Decode) - 80x36px
- • button.inline-flex.items-center (Copy output to clipboard) - 87x36px
- • button.inline-flex.items-center (Download output as text file) - 139x36px
- • button.inline-flex.items-center (Swap input and output) - 89x36px
- • button.inline-flex.items-center (Clear input and output) - 87x36px
Fix: Increase target size to at least 48x48 CSS pixels for touch interactions.
Social & Rich Results
-
Open Graph Basics Pass
Core Open Graph tags are present.
-
-
Twitter Card Pass
twitter:card set to summary_large_image.
-
Structured Data Warning
No JSON-LD schema scripts found.
Fix: Add JSON-LD structured data matching your page type (Organization, Article, Product, etc.).
-
PWA Metadata Warning
Manifest or Apple touch icon is missing.
Fix: Link your web app manifest and apple-touch-icon for improved install/share experiences.
-
Open Graph/Twitter Quality Warning
1 social preview quality issues detected.
- • ISSUE: og:title should typically be between 10 and 70 characters.
- • GUIDELINE: Optimal og:title length: 40-60 characters (acceptable: 10-70).
- • GUIDELINE: Optimal og:description length: 110-160 characters (acceptable: 50-200).
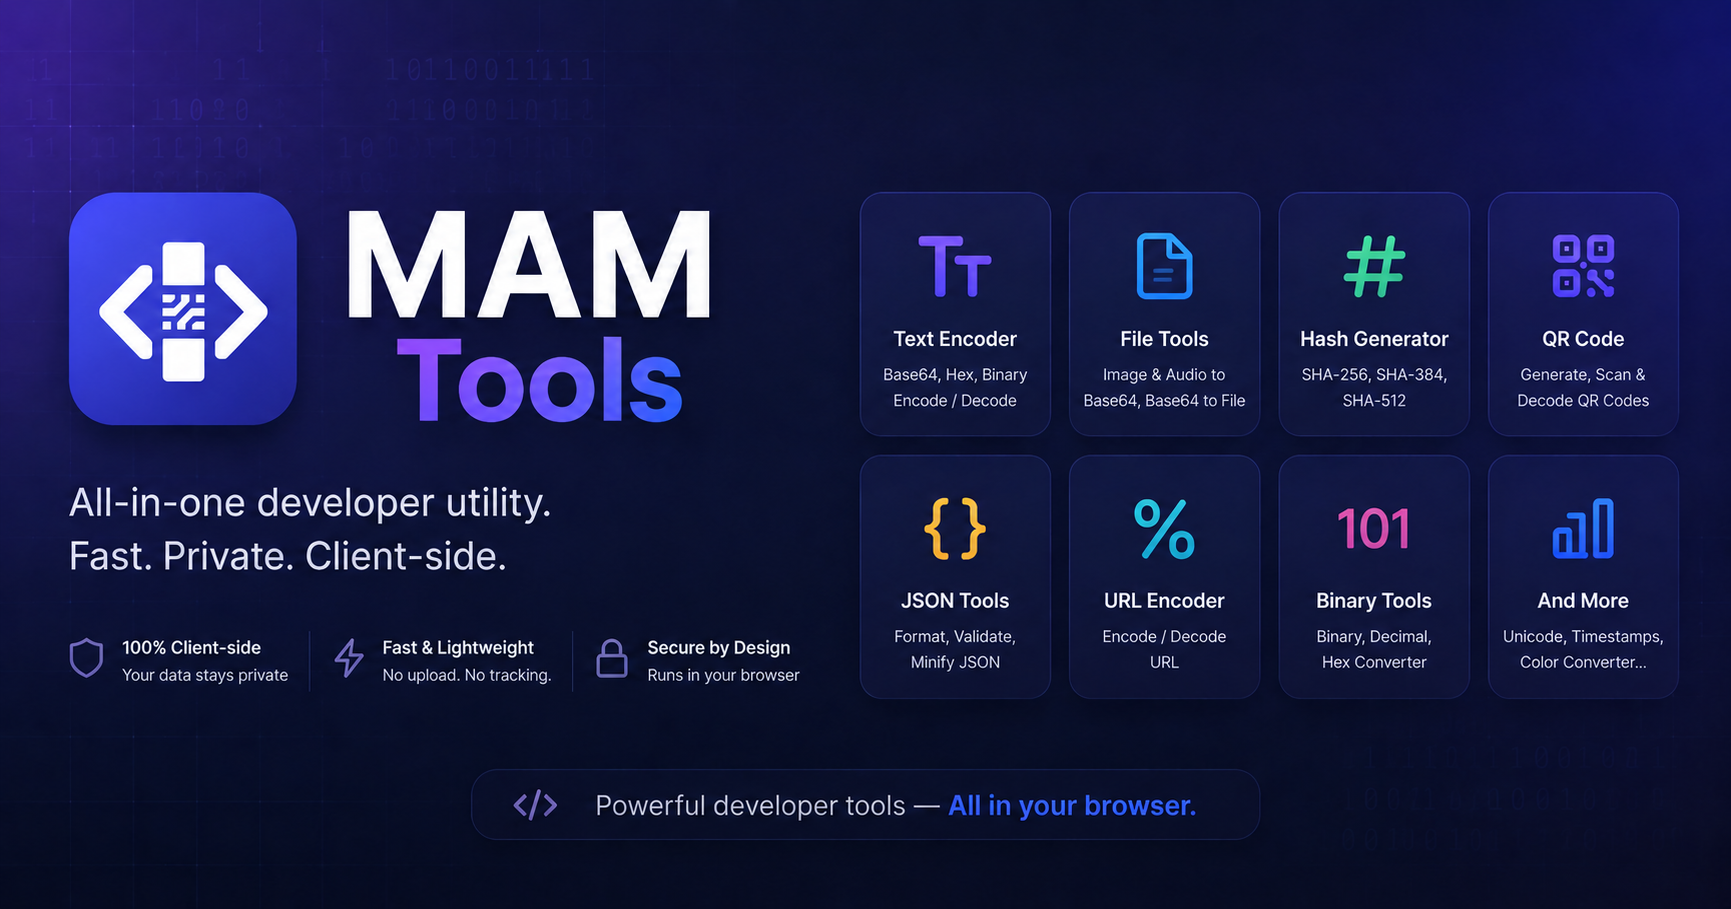
- • GUIDELINE: Optimal preview image size: 1200x630 pixels.
- • GUIDELINE: Optimal preview image aspect ratio: 1.91:1.
- • GUIDELINE: Optimal preview image file size: under 5 MB.
- • GUIDELINE: Recommended twitter:card: summary_large_image.
- • MEASURED: Image size: 1.32 MB
- • MEASURED: Image dimensions: 1731x909
Fix: Use absolute OG/Twitter URLs, keep metadata lengths in recommended ranges, and provide a preview image near 1200x630 under 5MB.
Links Analysis
-
Internal Links Pass
Checked 0 links. No broken internal links found.
-
External Links Pass
No broken external links found in checked URLs.
-
Link Format Pass
All 0 links use non-empty href values.
Performance & Runtime
-
Core Web Vitals: LCP Pass
Largest Contentful Paint: 0.24s.
-
Core Web Vitals: CLS Pass
Cumulative Layout Shift: 0.000.
-
Total Blocking Time estimate: 0ms.
-
Broken Assets Pass
No failed CSS/JS/image/font/media requests detected.
-
No console/page runtime errors detected during audit.